Structure for every part of compliance.
Requirements, documents, checks, insurance and people — connected, so each piece of evidence counts everywhere it should.
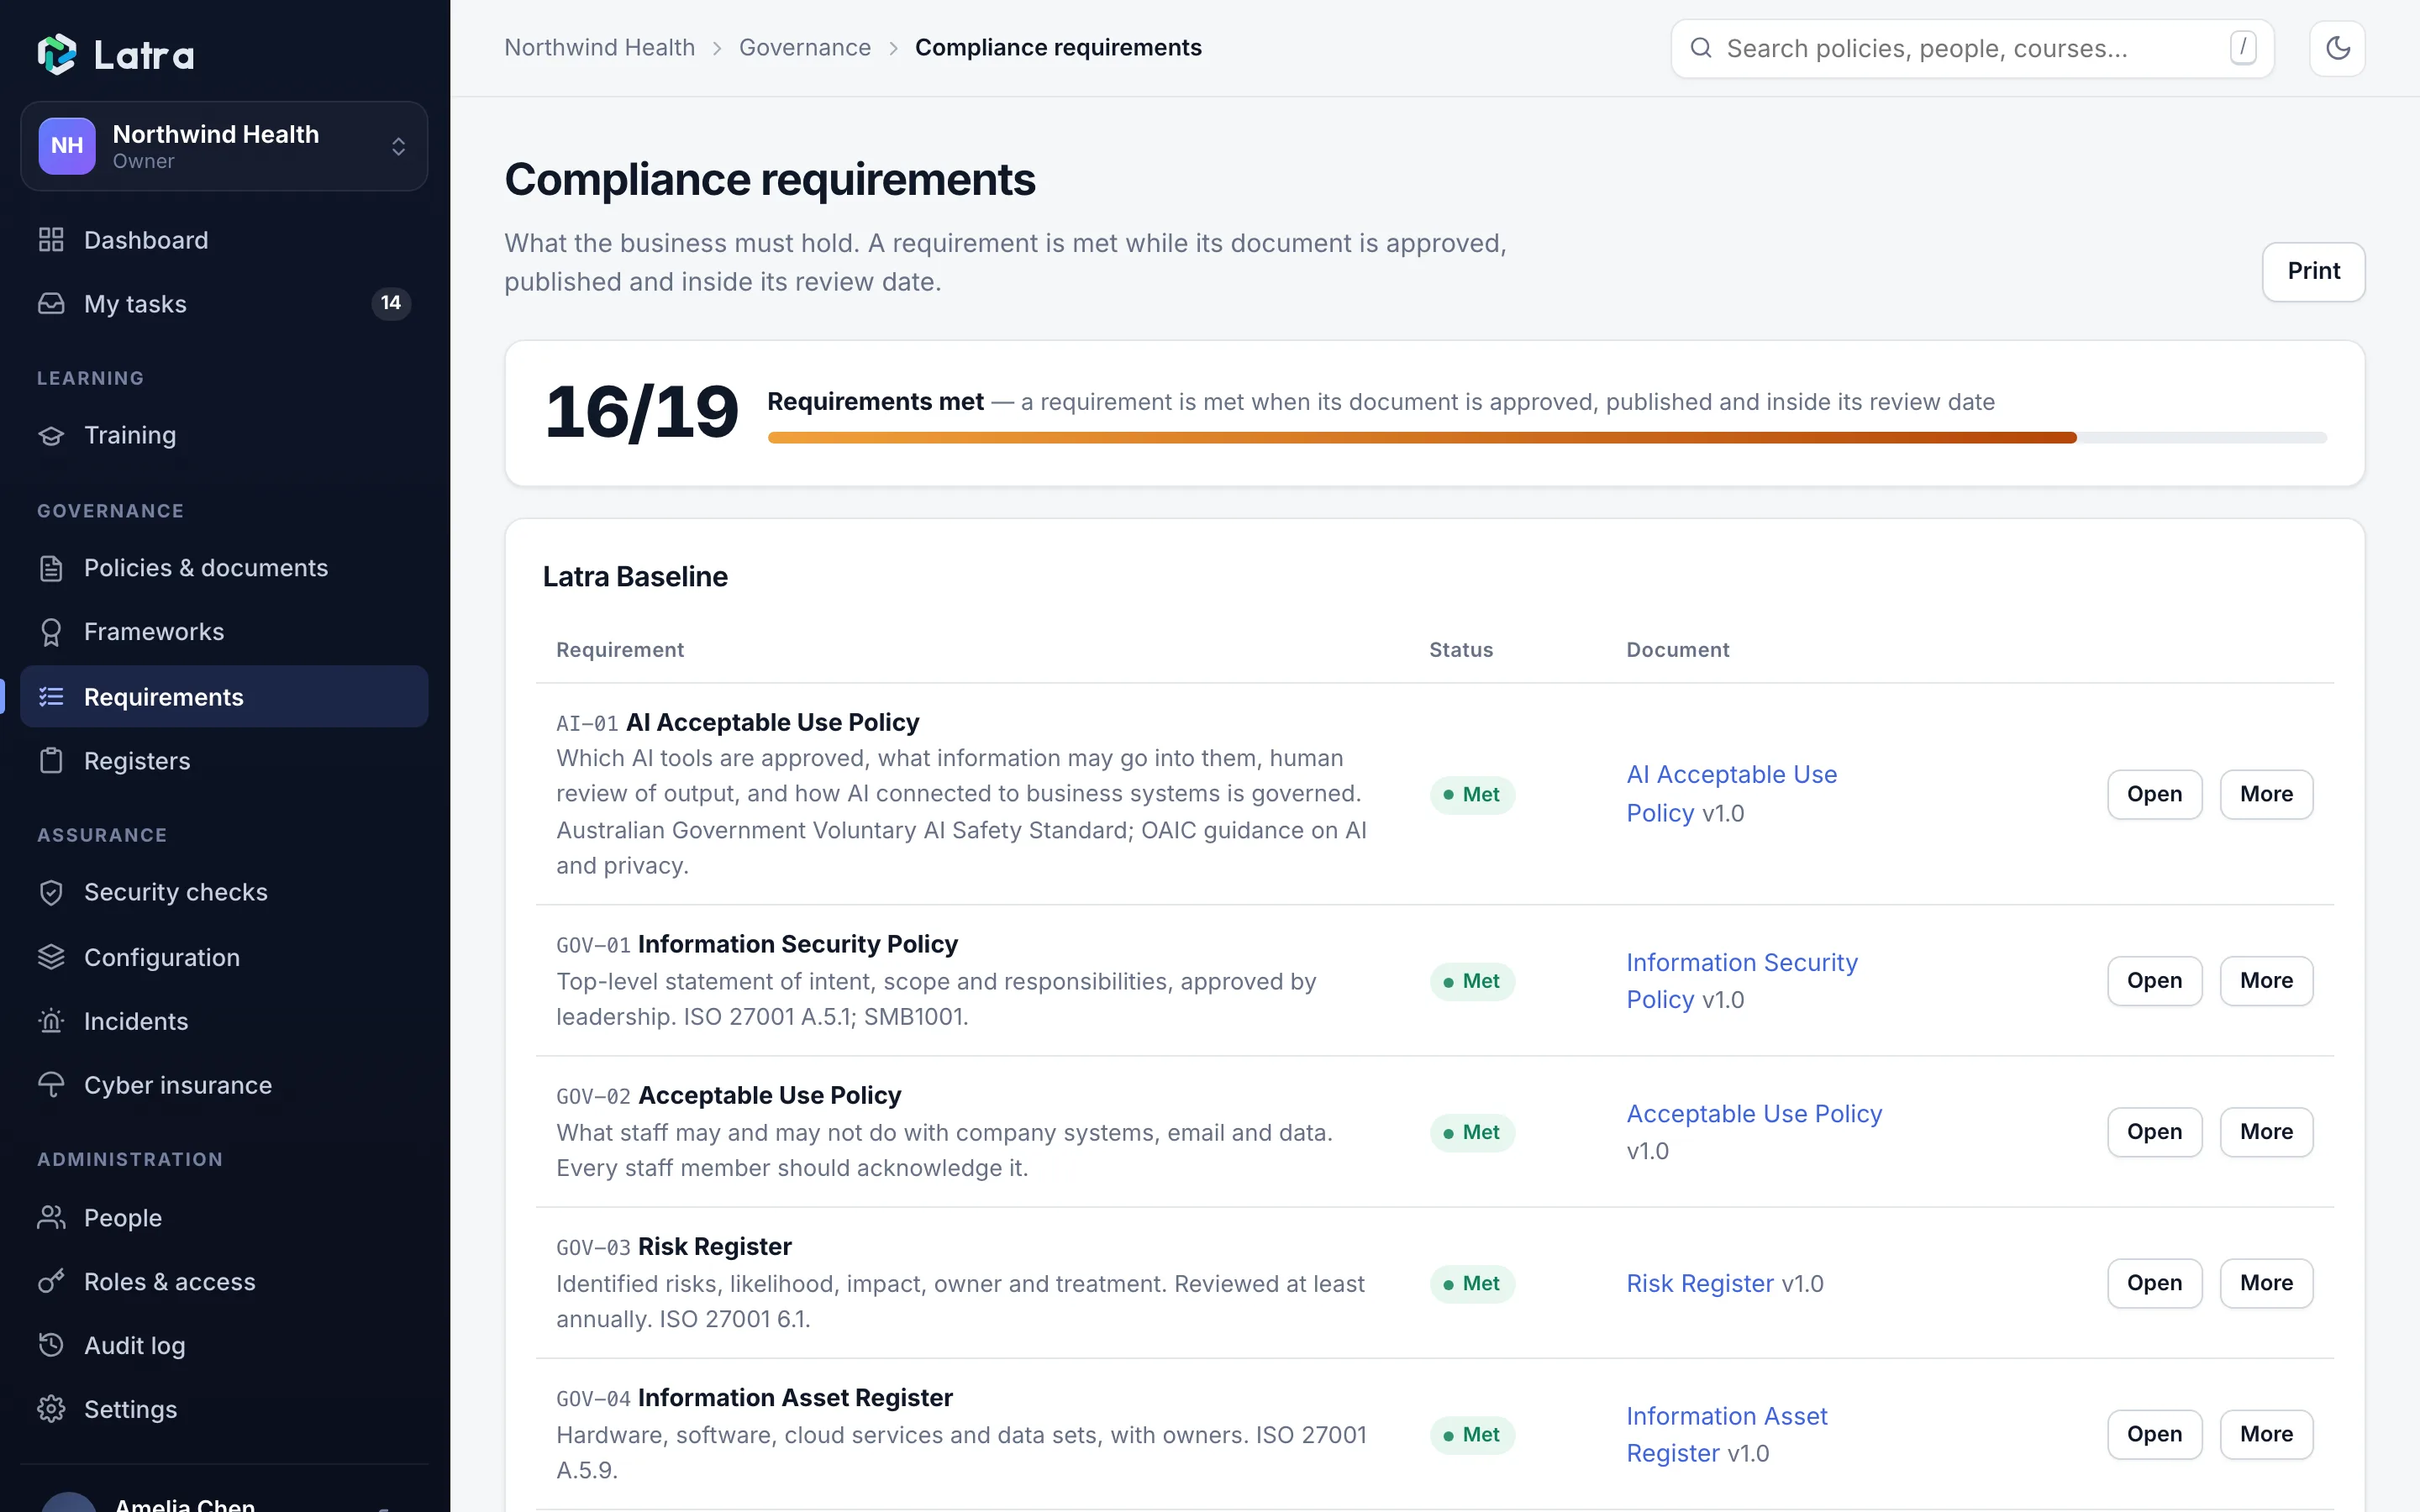
A baseline of what you should hold — already written down.
Latra starts every company with a baseline aligned to the Essential Eight, ISO 27001 and the Privacy Act. A requirement counts as met only while the document behind it is published and in date.
- Each requirement linked to the document that satisfies it
- Met, due for review, or missing — never guessed
- Framework references on every line
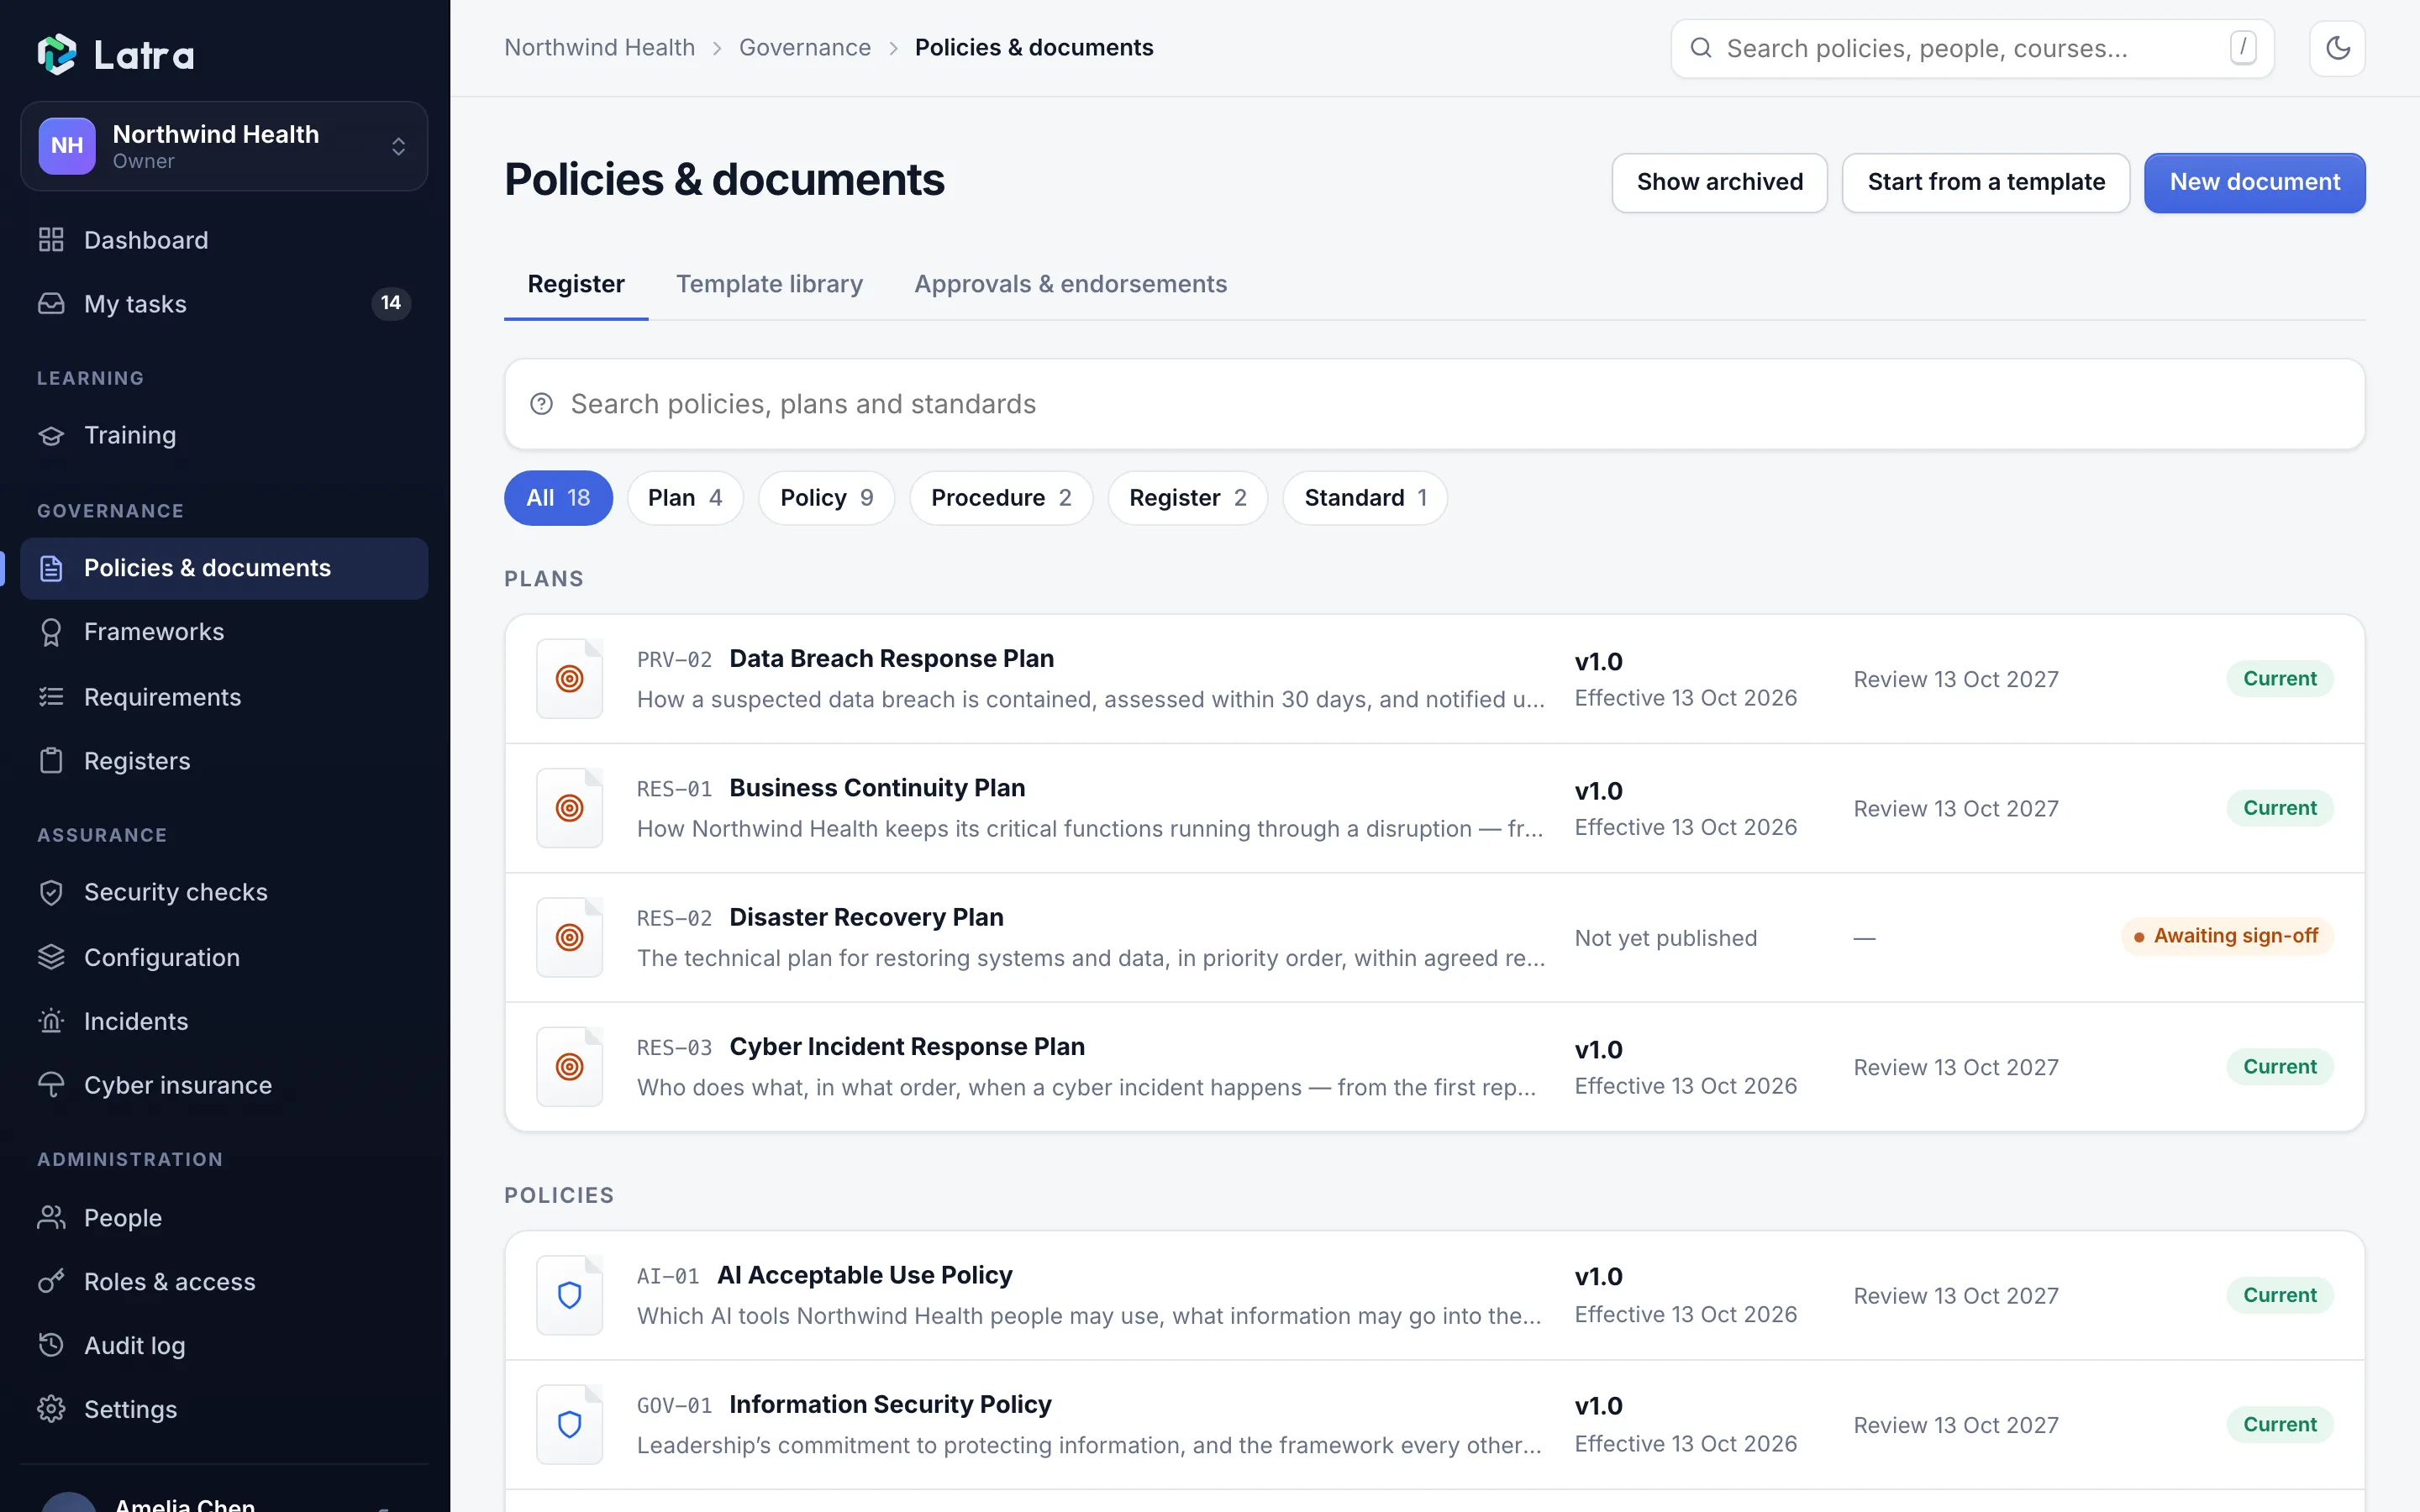
Controlled documents, not files in a drive.
Every policy, plan and standard is numbered, versioned and approved. Old versions are superseded, never overwritten, and review dates are tracked for you.
- Draft, review, approve, publish — with a record at every step
- Typed-name signatures bound to a fingerprint of the content
- Acknowledgement tracked per person, per version
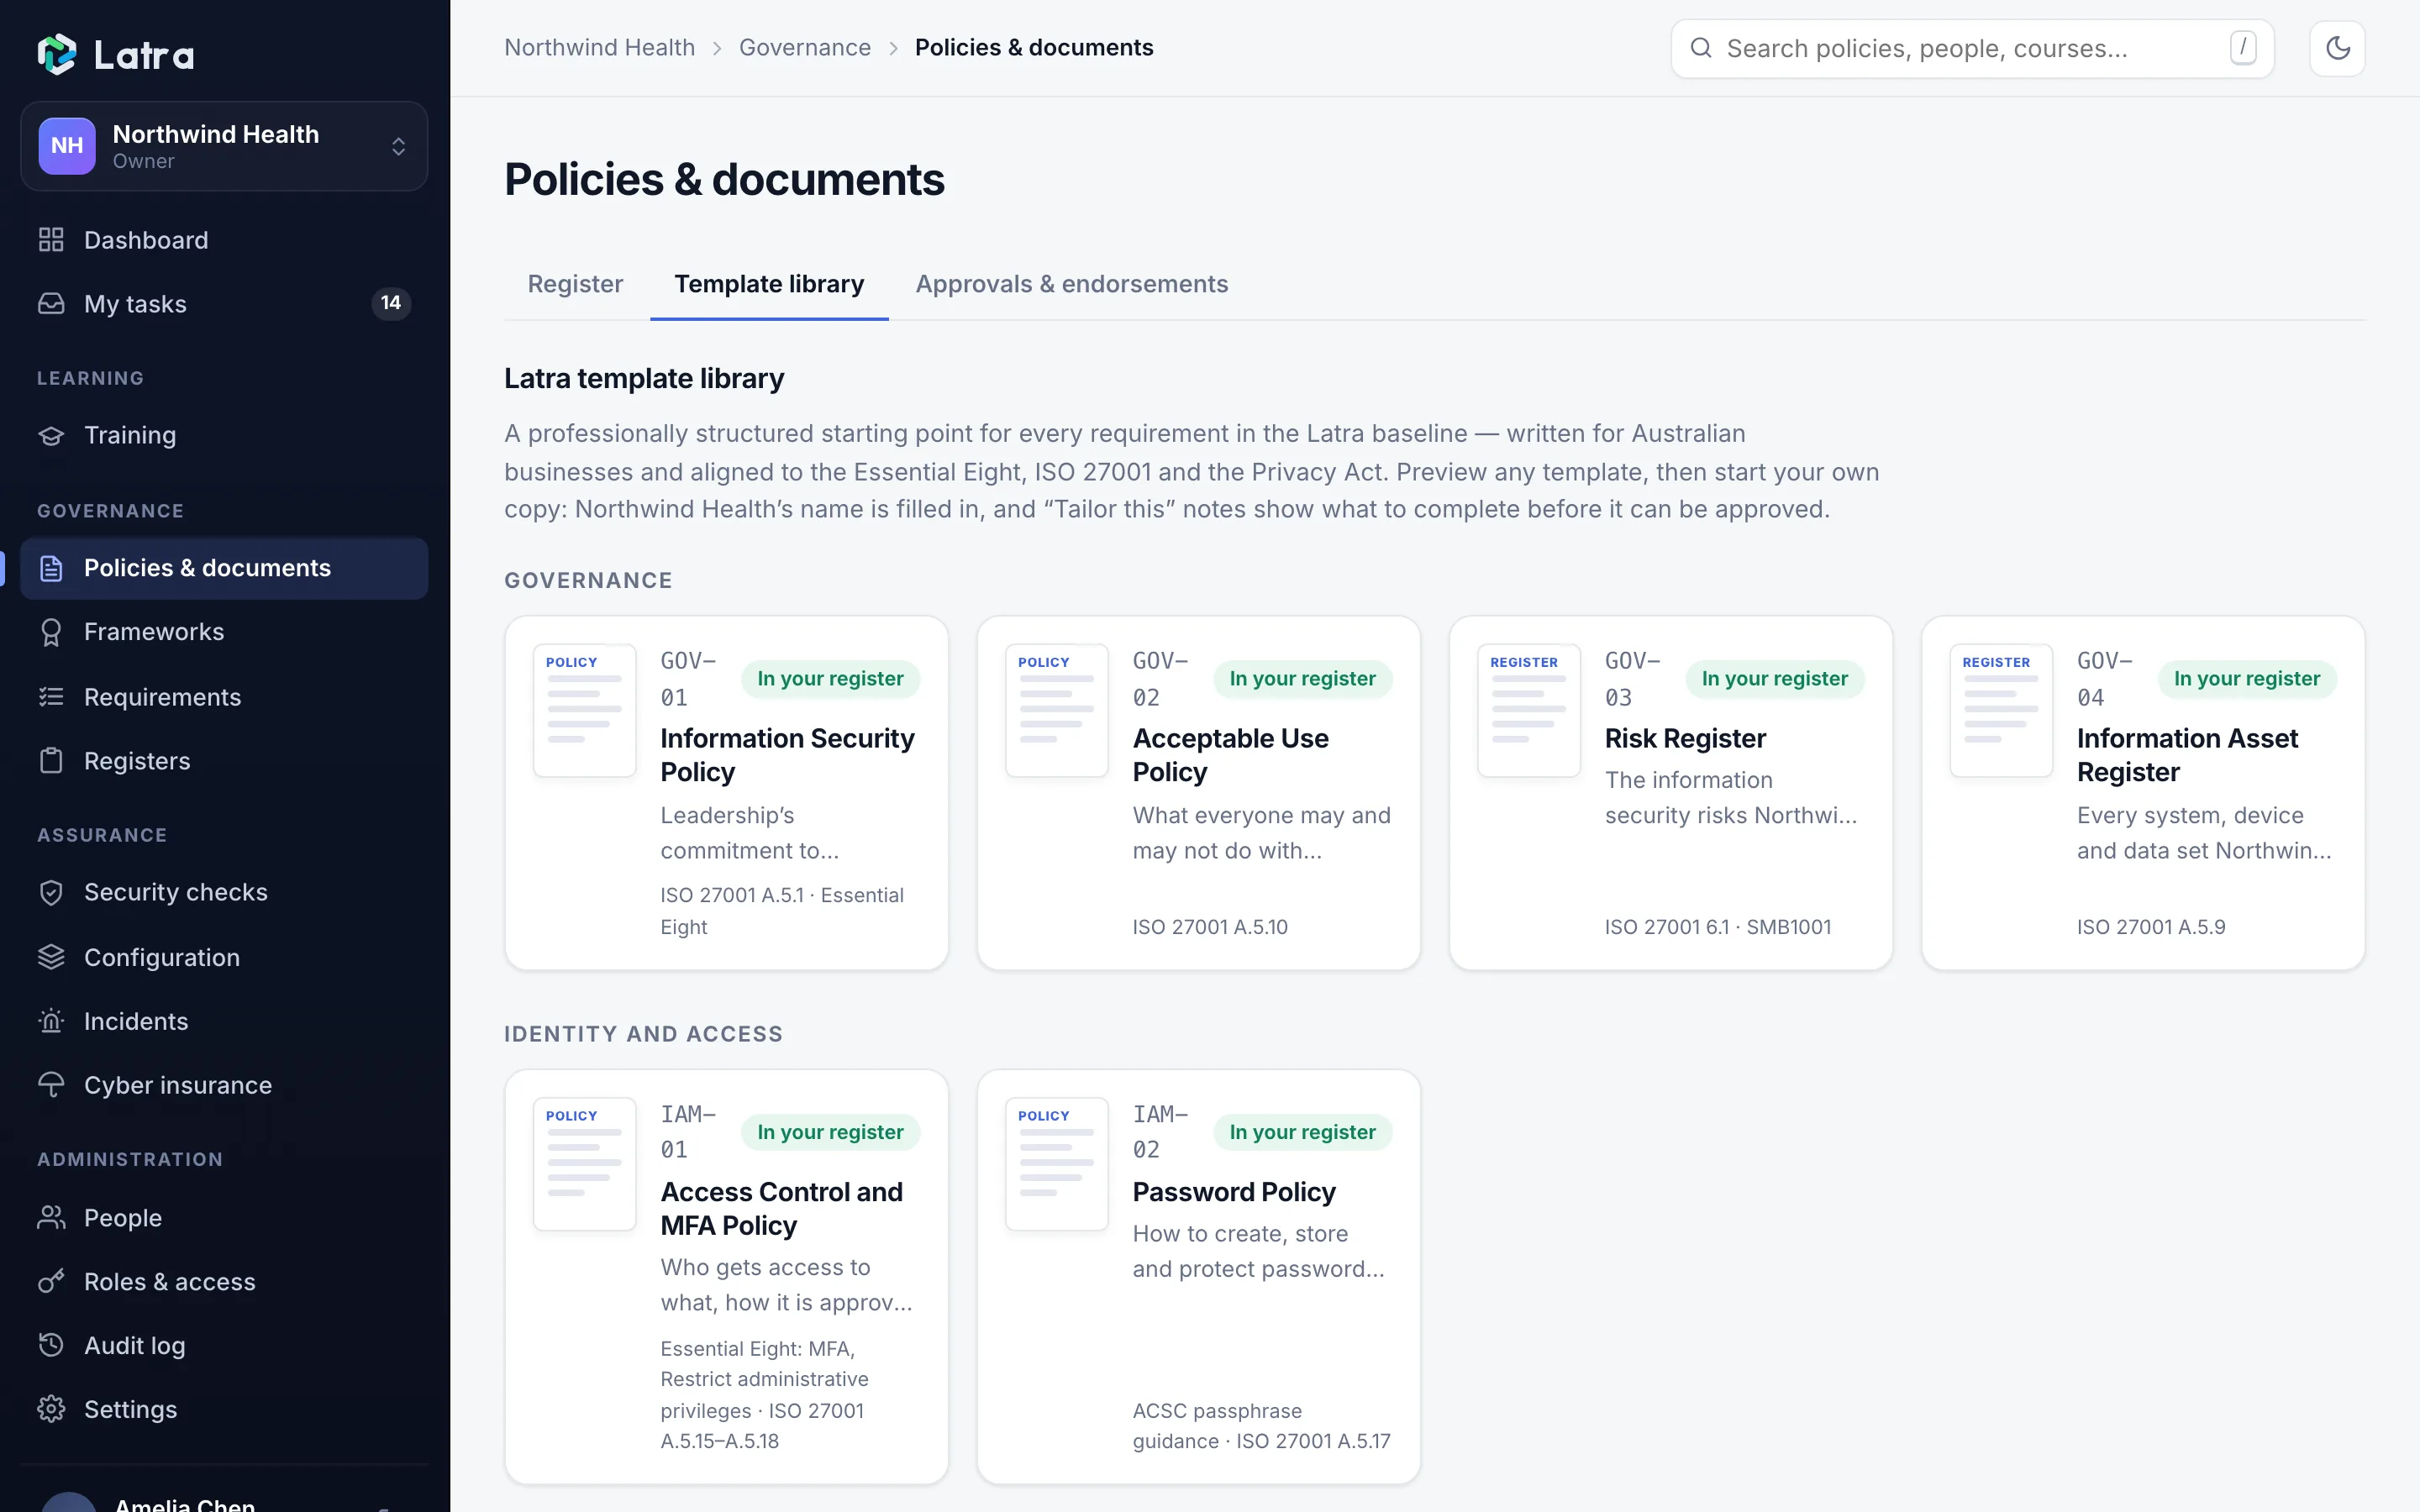
Nineteen templates, written for Australian businesses.
From an Information Security Policy to an AI Acceptable Use Policy. Your company name is filled in, and clearly marked notes show what to tailor — a document can’t be submitted until they’re done.
- Incident response, business continuity, access control and more
- Privacy and data breach response aligned to the Privacy Act
- Responsible AI use, aligned to the Voluntary AI Safety Standard
Every check, with its evidence and its verifier.
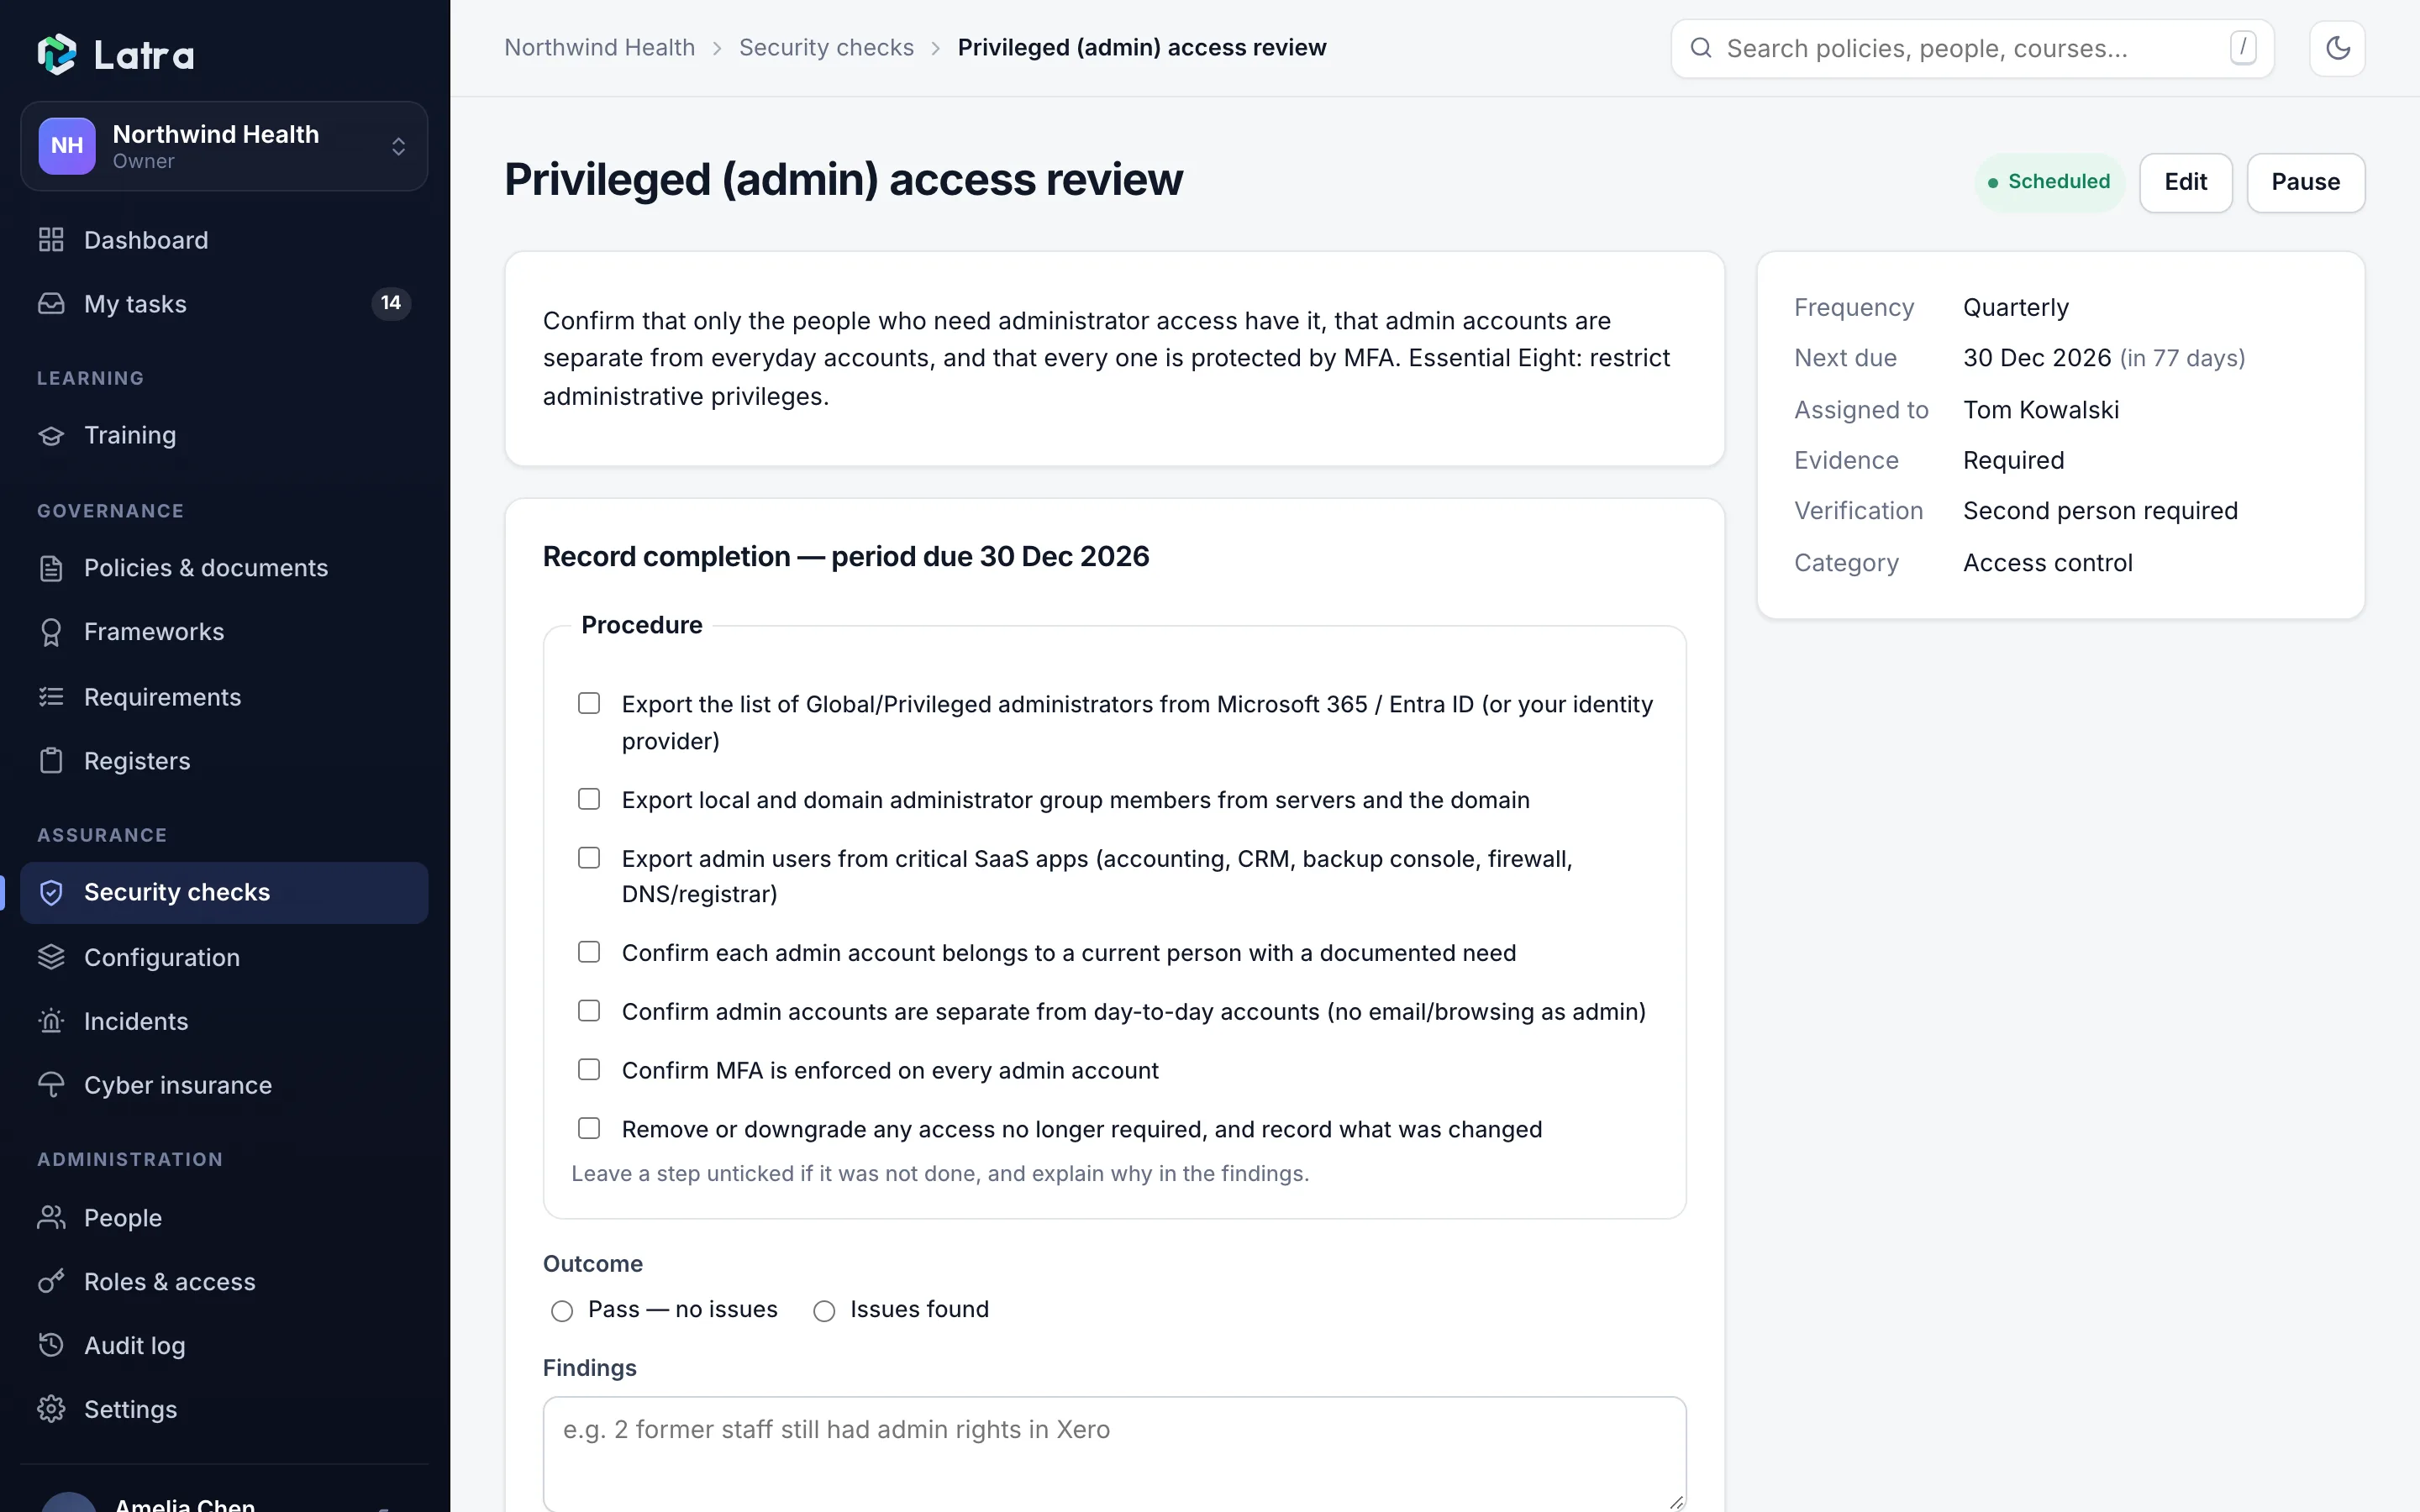
Each check has a procedure, an owner and a schedule. The person doing it records the result and attaches evidence; a second person can verify it.
- Procedures written step by step
- Exceptions recorded with a remediation note
- Completed records can’t be edited after the fact
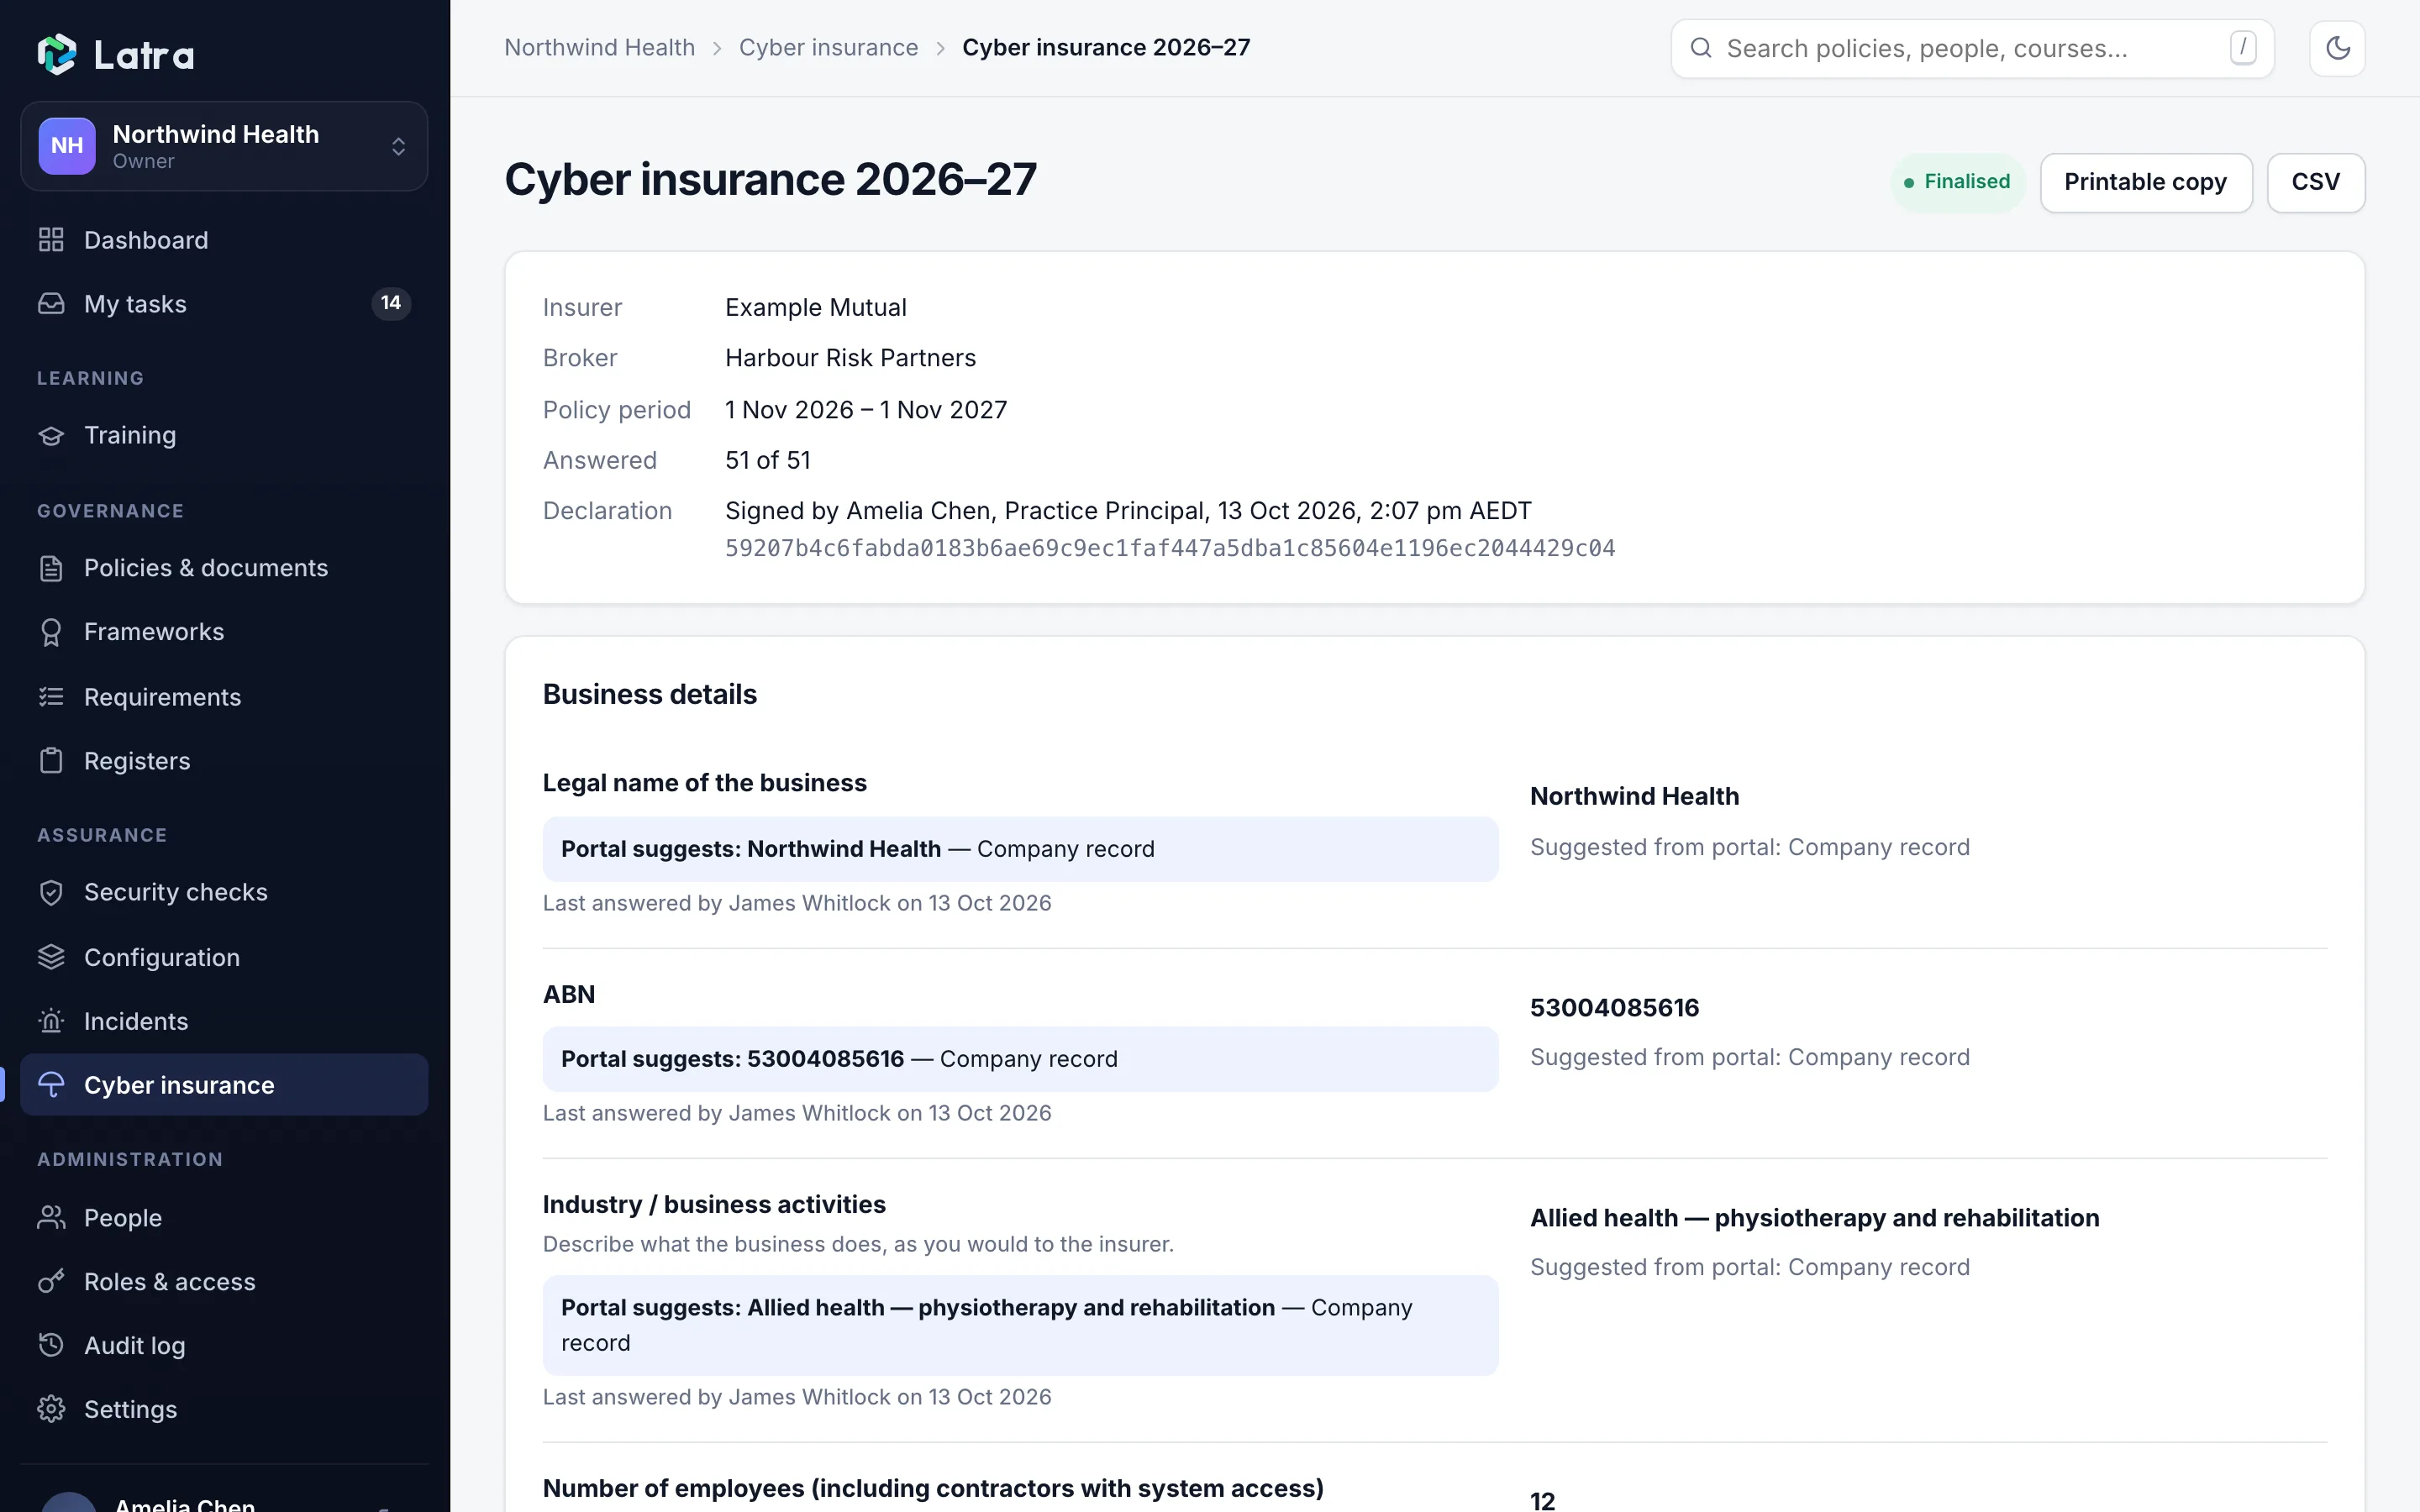
Answer the proposal from what you can prove.
Latra maps common insurer questions to your own records and shows the evidence for each suggested answer. A named person reviews and signs the declaration.
- Suggestions only where a record supports them
- Evidence shown beside every answer
- A signed, fingerprinted declaration
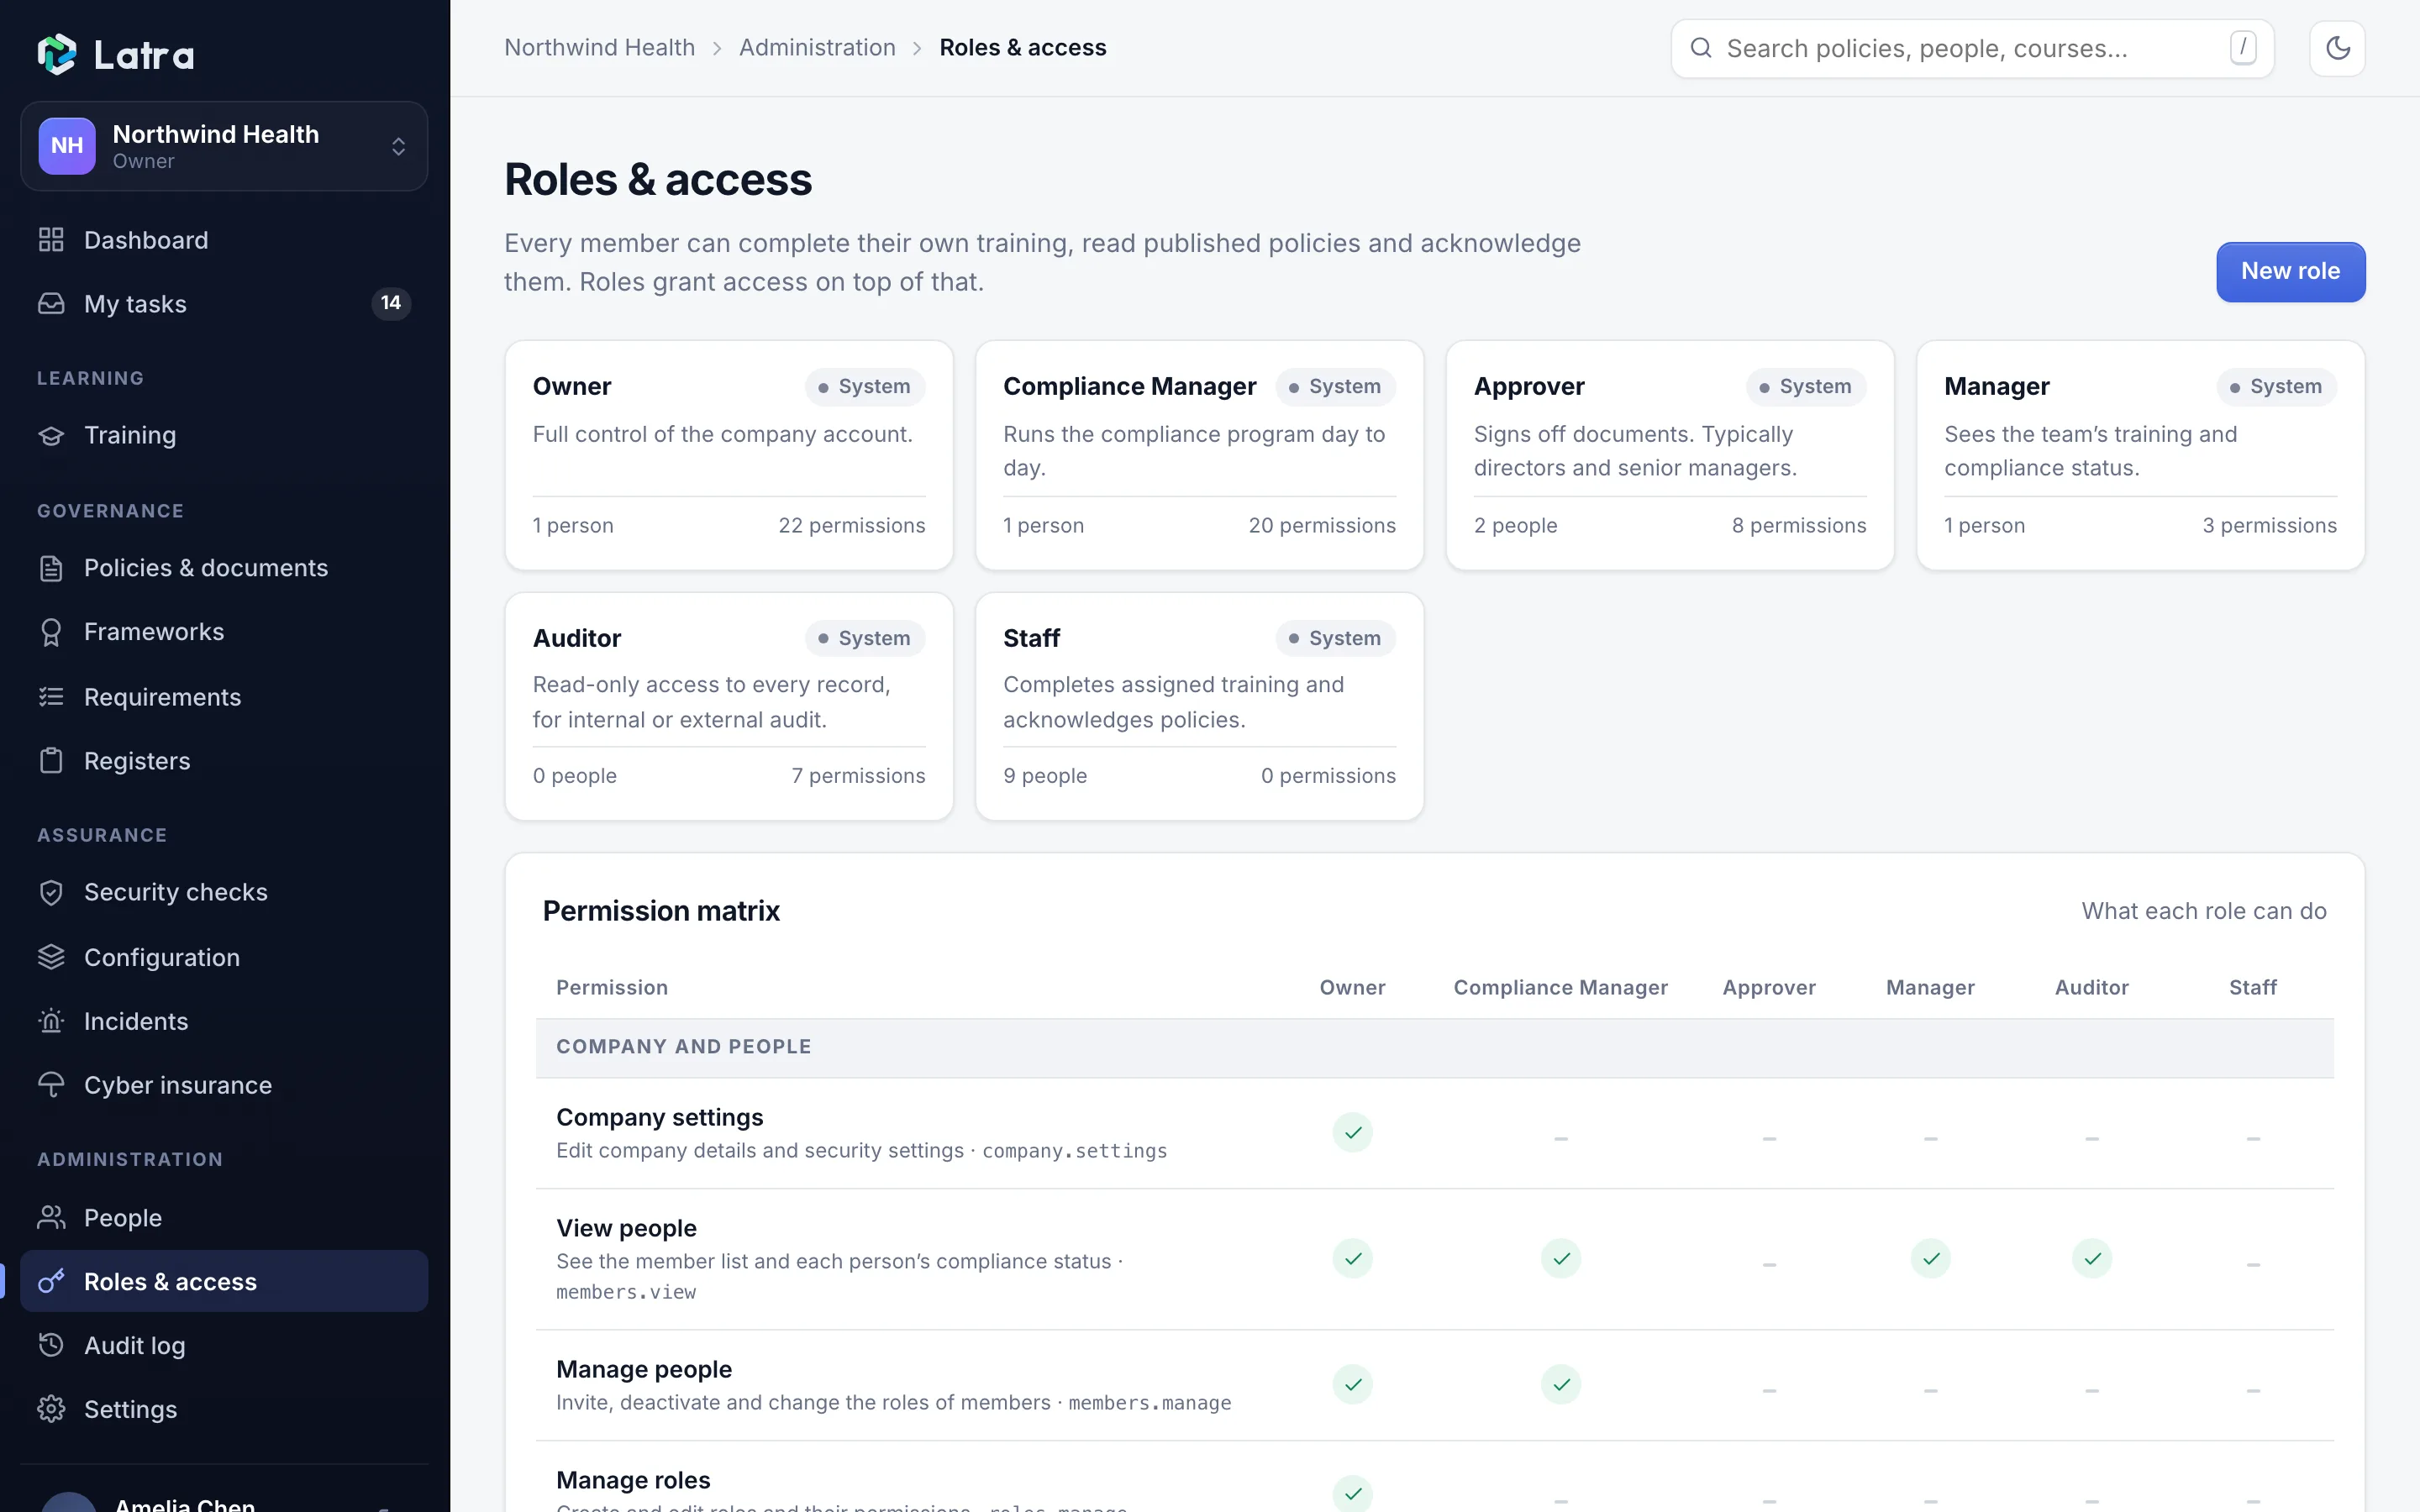
The right access for each person.
Owners, managers, approvers, staff and your IT provider each see what they need. Roles are built from clear permissions, and nobody can grant more than they hold.
- System roles, plus your own
- Invitations with two-step verification on by default
- Every grant and change recorded in the audit log